COBBLESTONE SOFTWARE
Contract Insight — User Guide
05. Advanced/User-Defined Permission Management
03. Admin User Manual › Employee/User Permissions › 05. Advanced/User-Defined Permission Management
Note: Each procedure in this guide begins at the Contract Insight homepage, so any section can be followed on its own. Custom fields are configurable, so the exact field list on a contract category record may vary between environments.
1. Overview
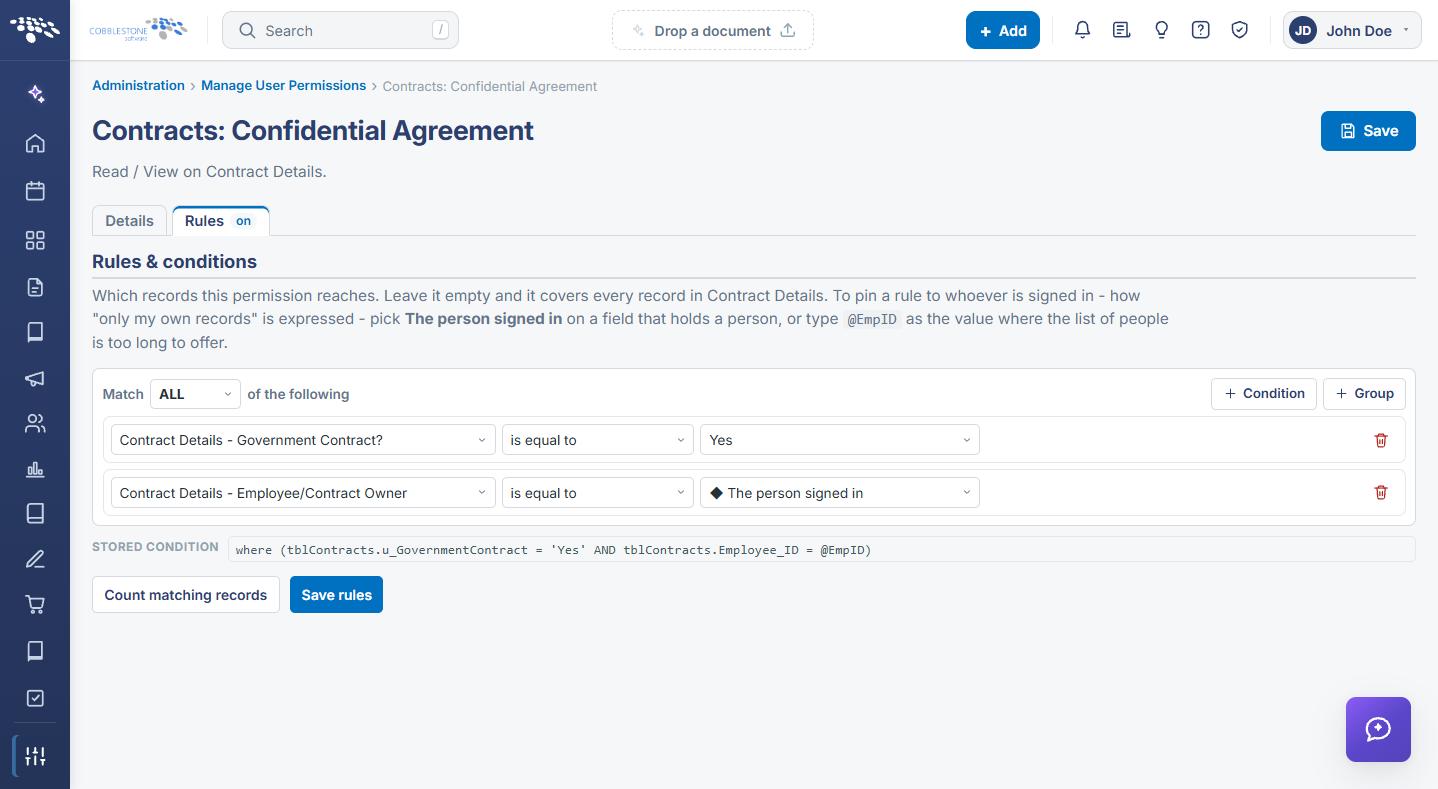
Beyond simply granting a permission, Manage User Permissions (Administration > Manage User Permissions) supports a full rules-and-conditions builder for scoping any permission to a subset of its area's records. Opening a permission's Rules tab shows a Match ALL/ANY-of-the-following condition list, where each condition picks a field, an operator (e.g. "is equal to"), and a value — including the special value "The person signed in" or an @EmpID placeholder for rules that should always resolve to whoever is currently logged in. The builder live-generates the equivalent SQL WHERE clause (labeled "Stored condition") and offers a "Count matching records" button to check how many records the rule currently resolves to before saving.
2. Key Elements
- Each permission in Manage User Permissions lists a Rules column showing whether it is scoped ("Limited by rules") or applies to every record in its area ("—").
- Opening a permission and switching to its Rules tab shows a "Match ALL / ANY of the following" condition builder, with "+ Condition" and "+ Group" controls for adding more rows or nested groups of conditions.
- Each condition row picks a field on the area (e.g. Contract Details — Entered By), a comparison operator (is equal to, and others), and a value; a value can be a literal, or the special "The person signed in" value, or an @EmpID placeholder to always mean whoever is currently signed in.
- The builder shows a live "Stored condition" line with the generated SQL WHERE clause (e.g. where (tblContracts.EnteredBy = 17887)) so the exact filter being applied is visible before saving.
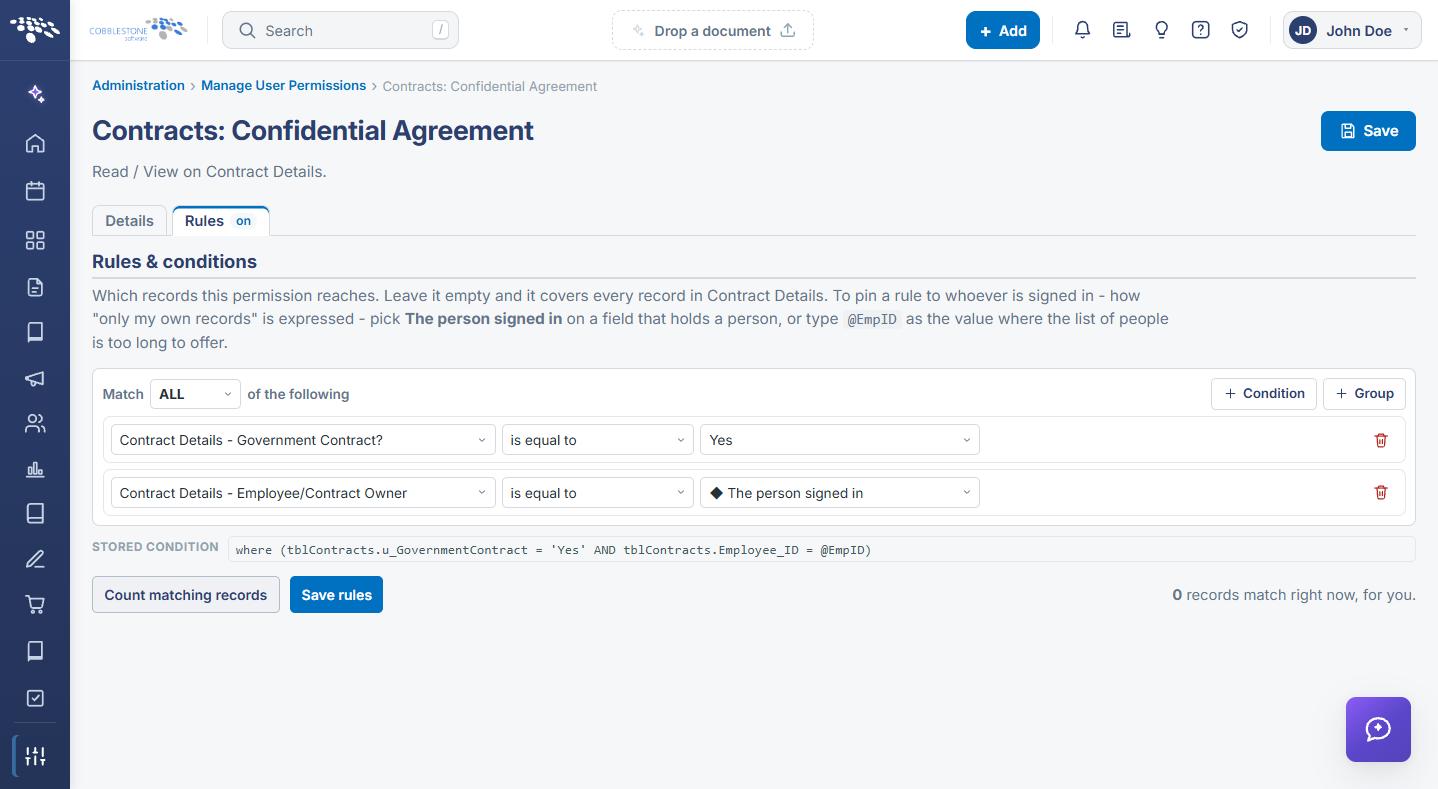
- A "Count matching records" button runs the current rule against live data and reports how many records it resolves to, letting an administrator verify scope before saving; "Save rules" commits the change.
3. Building a Rule with the Condition Builder
On a permission’s Rules tab, each row under "Match ALL/ANY of the following" picks a field on the permission’s area, an operator, and a value; + Condition adds another row and + Group nests a sub-group of conditions. As rows are added, the read-only Stored condition line below updates live with the exact SQL WHERE clause the rule will apply — for example, a rule matching a "Government Contract?" field equal to Yes, combined with "Employee/Contract Owner is equal to The person signed in," resolves to where (tblContracts.u_GovernmentContract = 'Yes' AND tblContracts.Employee_ID = @EmpID).
4. Checking How Many Records a Rule Matches
Before saving, Count matching records runs the rule as built against live data and reports a result inline (e.g. "0 records match right now, for you"), so the scope of a rule can be confirmed before it affects anyone’s access. Save rules commits the condition once it checks out.
5. Quick Reference Summary
| Action | Where |
|---|---|
| Open a permission’s rule builder | Administration → Manage User Permissions → Manage on a permission → Rules tab |
| See whether a permission is scoped at all | Manage User Permissions list → Rules column ("—" or "Limited by rules") |
| Add another condition to a rule | + Condition |
| Nest a sub-group of conditions | + Group |
| Match every condition vs. any one of them | Match ALL / ANY dropdown |
| Pin a condition to whoever is signed in | Value → The person signed in, or type @EmpID |
| See the exact filter a rule will apply | Stored condition line (generated SQL WHERE clause) |
| Check how many records a rule resolves to | Count matching records |
| Commit a rule change | Save rules |